TLDR workflow
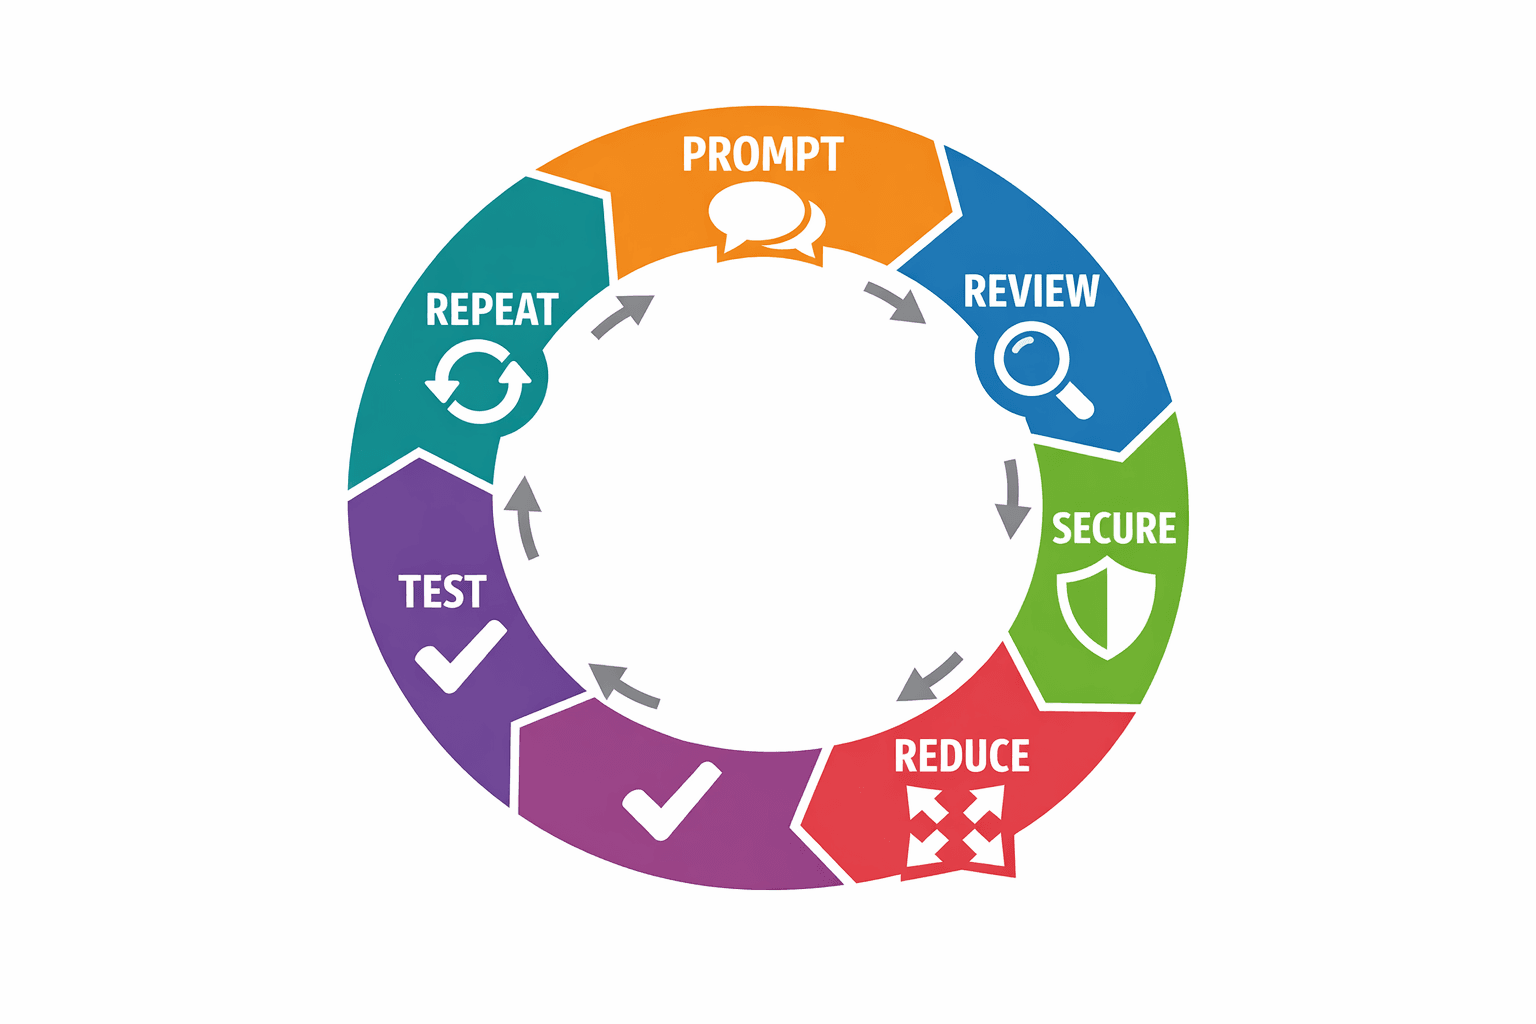
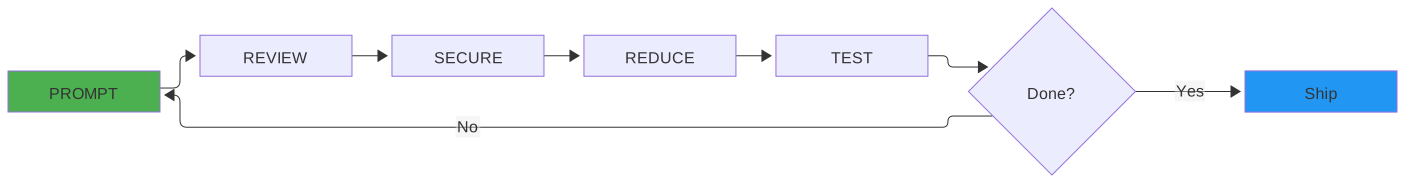
1. PROMPT   → One outcome, with a finish line
2. REVIEW   → Read the diff in a real diff viewer
3. SECURE   → Injection, secrets, auth, OWASP top 10
4. REDUCE   → Delete what isn't needed
5. TEST     → Automated tests plus a real smoke test
6. REPEAT   → Until it's production-ready, not just green
Example prompts:
PROMPT:   "Add logout button to navbar. Clear session, redirect to /login"
REVIEW:   "Show diff"
SECURE:   "/security-review"
REDUCE:   "Simplify, remove duplication"
TEST:     "Write tests for logout, run them"
REPEAT:   "Redirect broken on mobile Safari - fix"
Which steps are gates, which are judgment: enforce SECURE and TEST with hooks and CI, so nobody can skip them under a deadline. REVIEW and REDUCE are judgment calls. If you rush them, verbose AI code turns into long-term maintenance cost.
Signal to watch: frequent loops from REVIEW back to PROMPT usually mean weak context (missing CLAUDE.md rules, no reference code), not a weak model. Fix the context once instead of re-prompting again and again.